In this article
- 1. Why business risk management has become essential in Algeria
- 2. Risk management frameworks and process
- 3. Risk mapping, appetite and tolerance
- 4. Internal control and the three lines model
- 5. The role of executives, indicators and roadmap
- Conclusion: making business risk management a leadership reflex
- Frequently asked questions
A sharp devaluation, a container stuck in port, a failing sole supplier, a cyberattack or a poorly prepared tax audit: most of the crises we see in Algerian companies were not unforeseeable. They simply had not been anticipated. Business risk management is precisely about identifying these threats, and opportunities, before they materialise, then deciding deliberately what to accept, reduce, transfer or avoid.
For an executive, this is neither a compliance exercise nor a matter for specialists. It is a steering tool that protects value and secures growth. This guide covers the leading frameworks, the process, risk mapping, risk appetite, internal control and a practical roadmap, drawing on the experience we at Hodemia Consulting have built in Europe, the Gulf and Algeria.
1. Why business risk management has become essential in Algeria
A demanding environment
Algerian companies operate in a context where several families of risk overlap:
- Regulatory risk: frequent changes to tax, customs, foreign trade and sector rules, which must be tracked and applied without delay;
- Currency risk: movements in the dinar, access to foreign currency and domiciliation timelines weigh on importers and exporters alike;
- Supply risk: dependence on imported inputs, logistics delays, import controls;
- Reputational risk: a case amplified on social media can destroy in a few days an image built over twenty years;
- Cyber risk: ransomware, CEO fraud, data leaks, all the more sensitive since Law No. 25-11 on personal data protection;
- Compliance risk: AML/CFT under Law No. 05-01 as amended, corruption under Law No. 06-01, sector-specific obligations.
More demanding partners
Algeria's removal from the FATF grey list on 19 June 2026 does not ease the pressure. Correspondent banks, foreign investors and major clients now ask for evidence: a risk management policy, a risk map, a control framework. A company unable to produce them pays more for its financing, or loses business. The quality of risk management is also a pillar of good governance, as we explain in our guide to corporate governance in Algeria.
2. Risk management frameworks and process
Two complementary frameworks
Two international frameworks shape practice:
- ISO 31000:2018 (risk management guidelines): a short, universal text built around principles, an organisational framework and a process. It suits any organisation, whatever its size;
- COSO ERM 2017 (“Enterprise Risk Management – Integrating with Strategy and Performance”): five components and twenty principles linking risk to strategy, performance and governance.
There is no need to choose: we often recommend ISO 31000 for the method and COSO for the dialogue with the board.
The four steps of the process
- Identification: workshops with departments, analysis of past incidents, review of strategic objectives. The right question is not “what could go wrong?” but “what could stop us from achieving our objectives?”;
- Assessment: scoring each risk by likelihood and impact (financial, operational, regulatory, reputational), first as gross risk, then as net risk after taking existing controls into account;
- Treatment: avoid, reduce, transfer (insurance, contract clauses) or accept, with an action plan, an owner and a deadline;
- Monitoring: periodic review, indicators, incident reporting and an update at least once a year.
3. Risk mapping, appetite and tolerance
The risk map as a dialogue tool
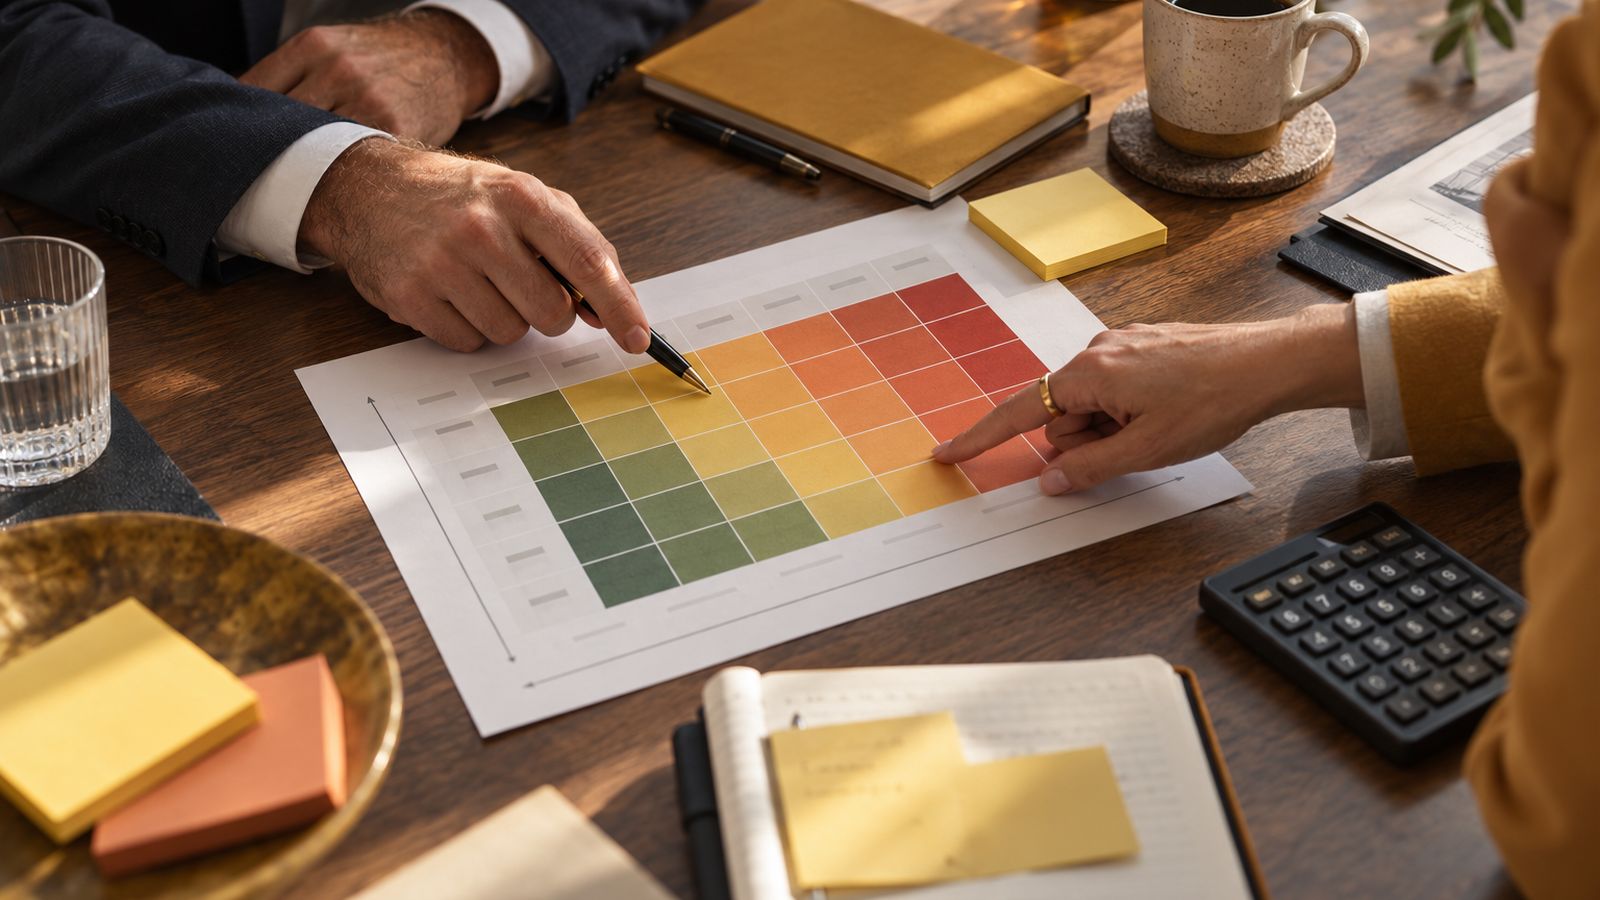
A risk map plots each risk on a likelihood-impact matrix, often with four or five levels. Its value lies not in how attractive the chart looks, but in the discussion it sparks: why does finance consider currency risk critical while sales sees it as moderate? A useful risk map fits on one page for the board, with a top 10 of major risks, and is broken down by department for operational management.
Two pitfalls recur in our engagements. The first: an overly generic map, copied from a template, listing “country risk” or “economic risk” with no link to the company's actual objectives. The second: a static map, produced once for an auditor or a lender, then left in a drawer. A living risk map is reviewed after every significant incident, every acquisition and every major regulatory change.
Risk appetite and tolerance
Risk appetite is the amount and type of risk the company is willing to take to achieve its objectives. It is set by the board of directors and expressed in a few clear statements. Tolerance translates it into measurable thresholds. Examples:
| Area | Appetite statement | Tolerance threshold |
|---|---|---|
| Compliance | No appetite for deliberate breaches of the law | Zero sanctions for AML/CFT failings |
| Supply | Low appetite for supplier dependence | No supplier above 30% of purchases |
| Growth | Moderate appetite for new markets | Investment capped at a percentage of equity |
Without a formal risk appetite, every decision is made case by case, depending on individual sensitivities.
4. Internal control and the three lines model
Internal control, the operational arm of risk management
Internal control covers the policies, procedures and controls that bring risks down to an acceptable level: segregation of duties, dual signatures, reconciliations, IT access rights, supplier reviews. For banks and financial institutions, Bank of Algeria Regulation No. 11-08 of 28 November 2011 sets the framework: control of transactions and internal procedures, accounting organisation, risk measurement and monitoring systems, compliance control and reporting to governing bodies. For other companies, this text is a useful source of inspiration, even though it does not apply to them.
The three lines model
Updated by the Institute of Internal Auditors (IIA) in July 2020, this model clarifies who does what:
- First line: operational staff, the risk owners, who apply controls day to day;
- Second line: the risk, compliance and permanent control functions, which provide the methodology, advise and challenge;
- Third line: internal audit, which gives the board independent assurance on the whole framework.
In many Algerian companies, these roles overlap: the management controller acts as risk manager and internal audit performs first-level checks. Clarifying roles is often the first gain. A compliance assessment helps bring these overlaps to light objectively and prioritise corrections.
5. The role of executives, indicators and roadmap
The board and senior management
The board of directors sets risk appetite, approves the map of major risks and ensures, often through an audit or risk committee, that the framework works. Senior management is responsible for it day to day: it appoints risk owners, allocates resources and makes trade-offs. Its example is decisive: if the CEO personally bypasses procedures, no framework will hold.
Key risk indicators (KRIs)
KRIs are early warning signals, distinct from performance indicators. A few examples:
- share of the largest supplier in total purchases;
- average customs clearance time for critical inputs;
- open currency position relative to profit;
- number of phishing attempts detected and click rate during tests;
- number of high-risk customer files not reviewed on time.
Each KRI should be linked to an alert threshold consistent with risk tolerance and to a predefined action.
Roadmap for an SME
- Months 1-2: management workshop, identification and scoring of the ten main risks;
- Months 3-4: appointment of an owner for each risk, action plans for the three priority risks;
- Months 5-6: a few simple KRIs, six-monthly review by the management committee.
Roadmap for a group
- Phase 1: risk management policy approved by the board, risk appetite statement, appointment of a risk manager reporting to senior management;
- Phase 2: risk maps for each subsidiary and group consolidation, common scoring methodology;
- Phase 3: integration into budgeting and strategy, KRI dashboard, risk-based internal audit plan.
In the Gulf, we have seen family groups complete these steps in eighteen to twenty-four months. The key is not the software, but genuine board involvement.
Conclusion: making business risk management a leadership reflex
Business risk management is not one more constraint: it is the ability to decide faster and more safely in an uncertain environment. A clear process, a shared risk map, a formal risk appetite, internal control organised along the three lines and a few well-chosen indicators are enough to change the game. Start small, but start now: the next crisis will not give you notice.
FAQ: business risk management
Does an Algerian SME really need a risk management approach?
Yes, even if it does not need a bank's tooling. An SME is often more vulnerable than a large group: dependence on one customer or supplier, tight cash flow, a key person. A simple map of the ten main risks, an owner for each risk and a six-monthly review by the management committee are enough to get started and quickly lead to safer decisions.
Do you have to choose between COSO ERM and ISO 31000?
No. The two frameworks are compatible. ISO 31000:2018 offers short, universal guidelines suited to any organisation. COSO ERM 2017 places more emphasis on the link between risk, strategy and performance, and on the role of the board. Many companies draw on ISO 31000 for the process and on COSO for governance and dialogue with the board of directors.
What is the difference between risk appetite and risk tolerance?
Risk appetite expresses, at board level, the type and overall level of risk the company accepts in pursuit of its objectives. Tolerance translates that appetite into measurable thresholds by activity or indicator, for example a cap on dependence on a single supplier. Breaching a tolerance triggers an alert and a documented decision by senior management.
Is internal control mandatory in Algeria?
For banks and financial institutions, yes: Bank of Algeria Regulation No. 11-08 of 28 November 2011 requires them to operate a comprehensive internal control system. For other companies, no general text sets out its detailed content, but sound internal control remains essential to make financial information reliable, prevent fraud and reassure banks, auditors and investors.
Who should own risk management within the company?
The board of directors sets risk appetite and oversees the framework. Senior management is responsible for it day to day and decides on risk treatment. Each operational director owns their risks. A risk manager, even part-time in an SME, runs the methodology and consolidates reporting, while internal audit provides independent assurance.

Nearly 20 years of international experience in regulatory compliance, risk and governance (EY in Luxembourg, San Francisco and London; Director, Regulatory & Compliance Services at KPMG Middle East). Certified coach, trainer and academic.